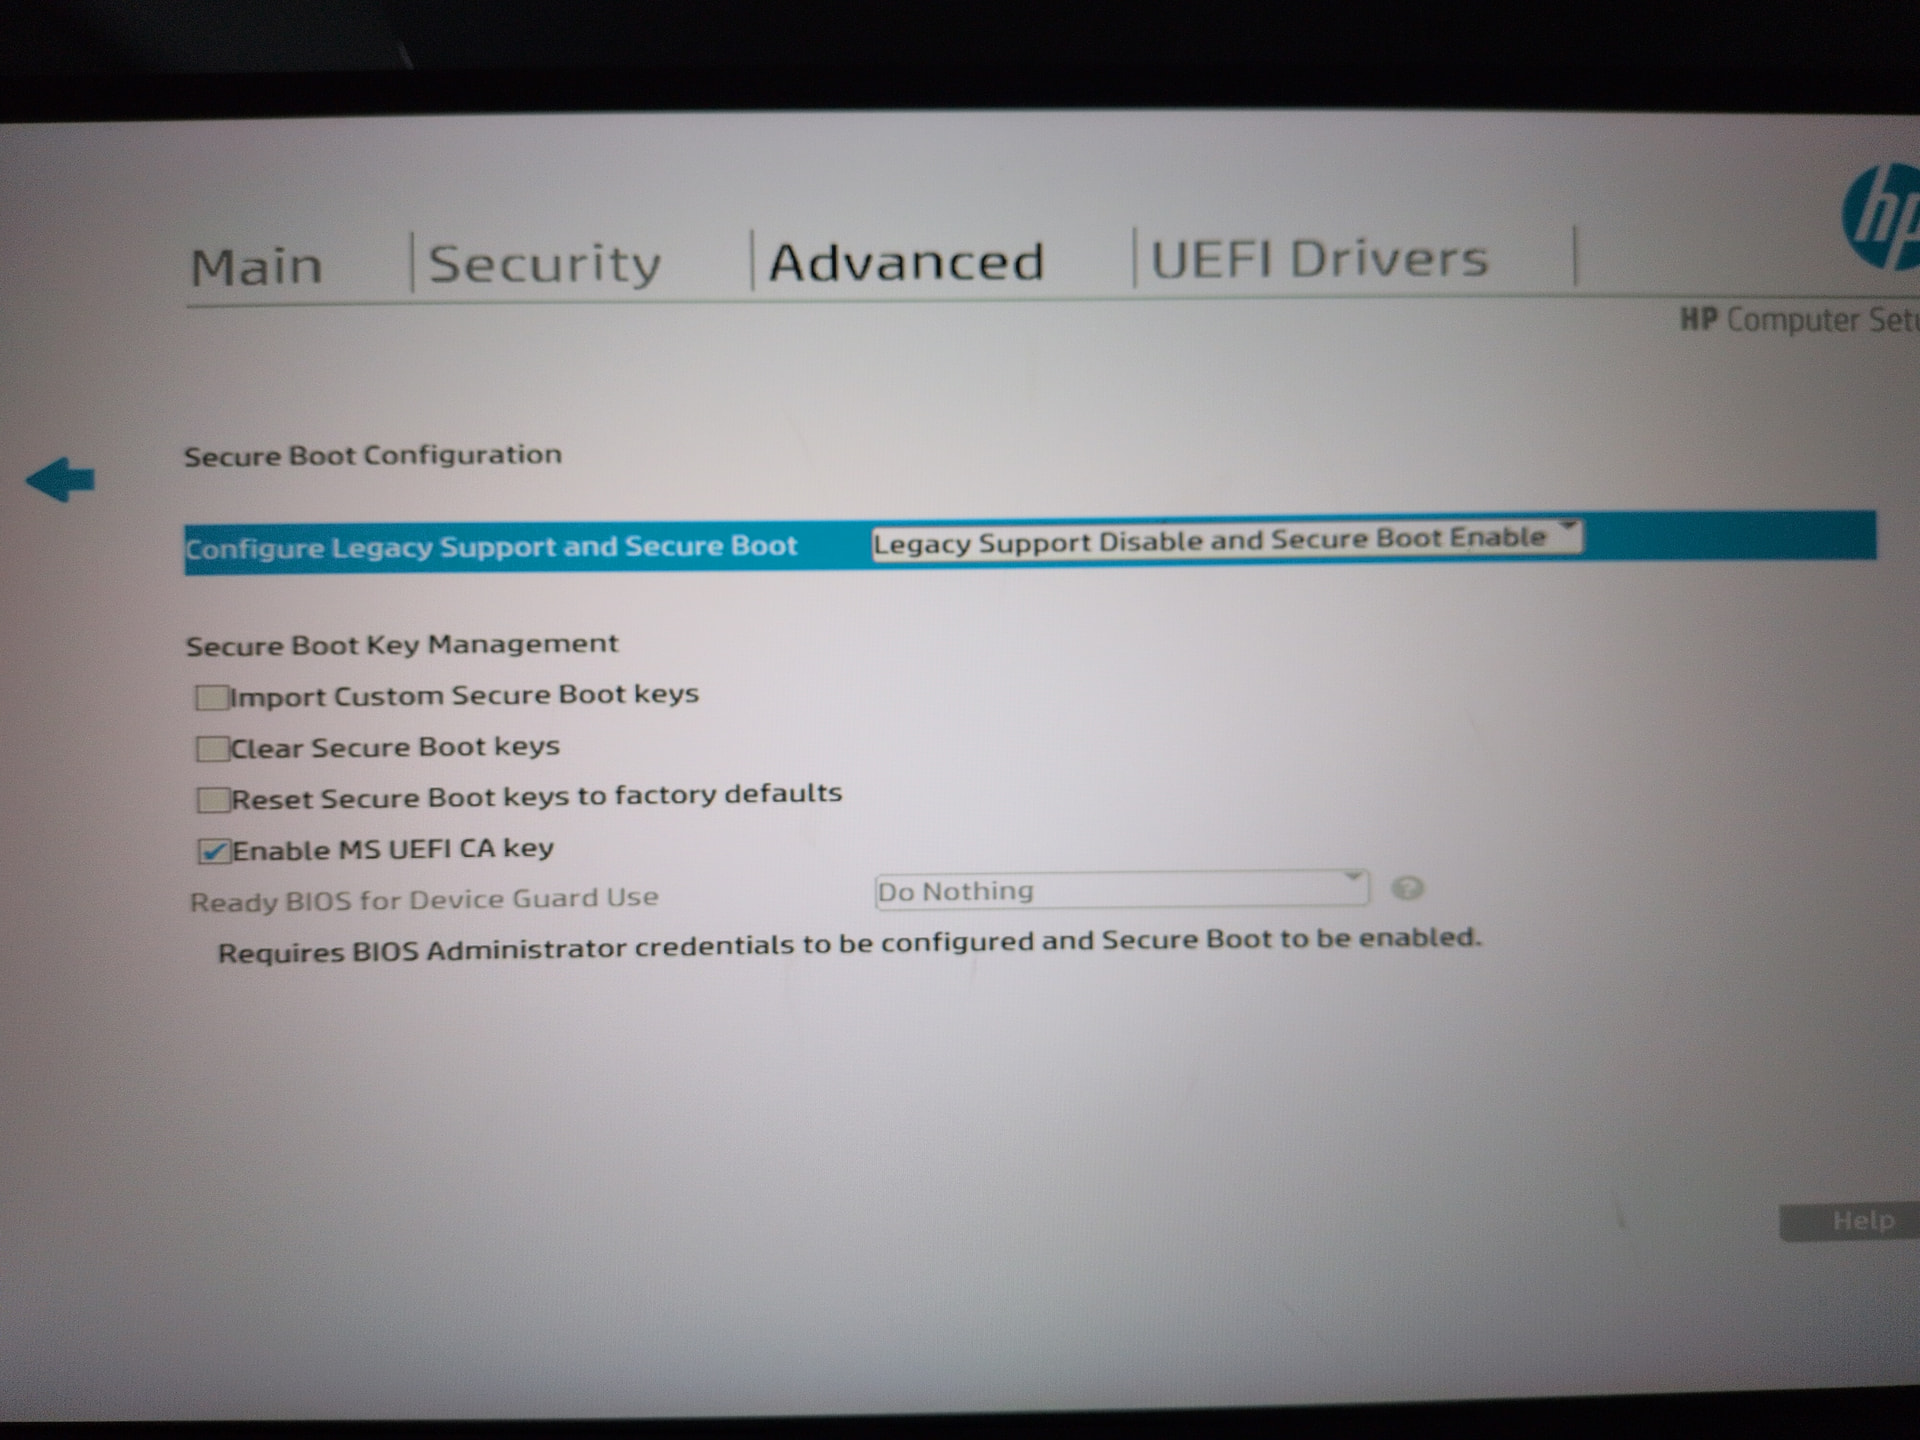
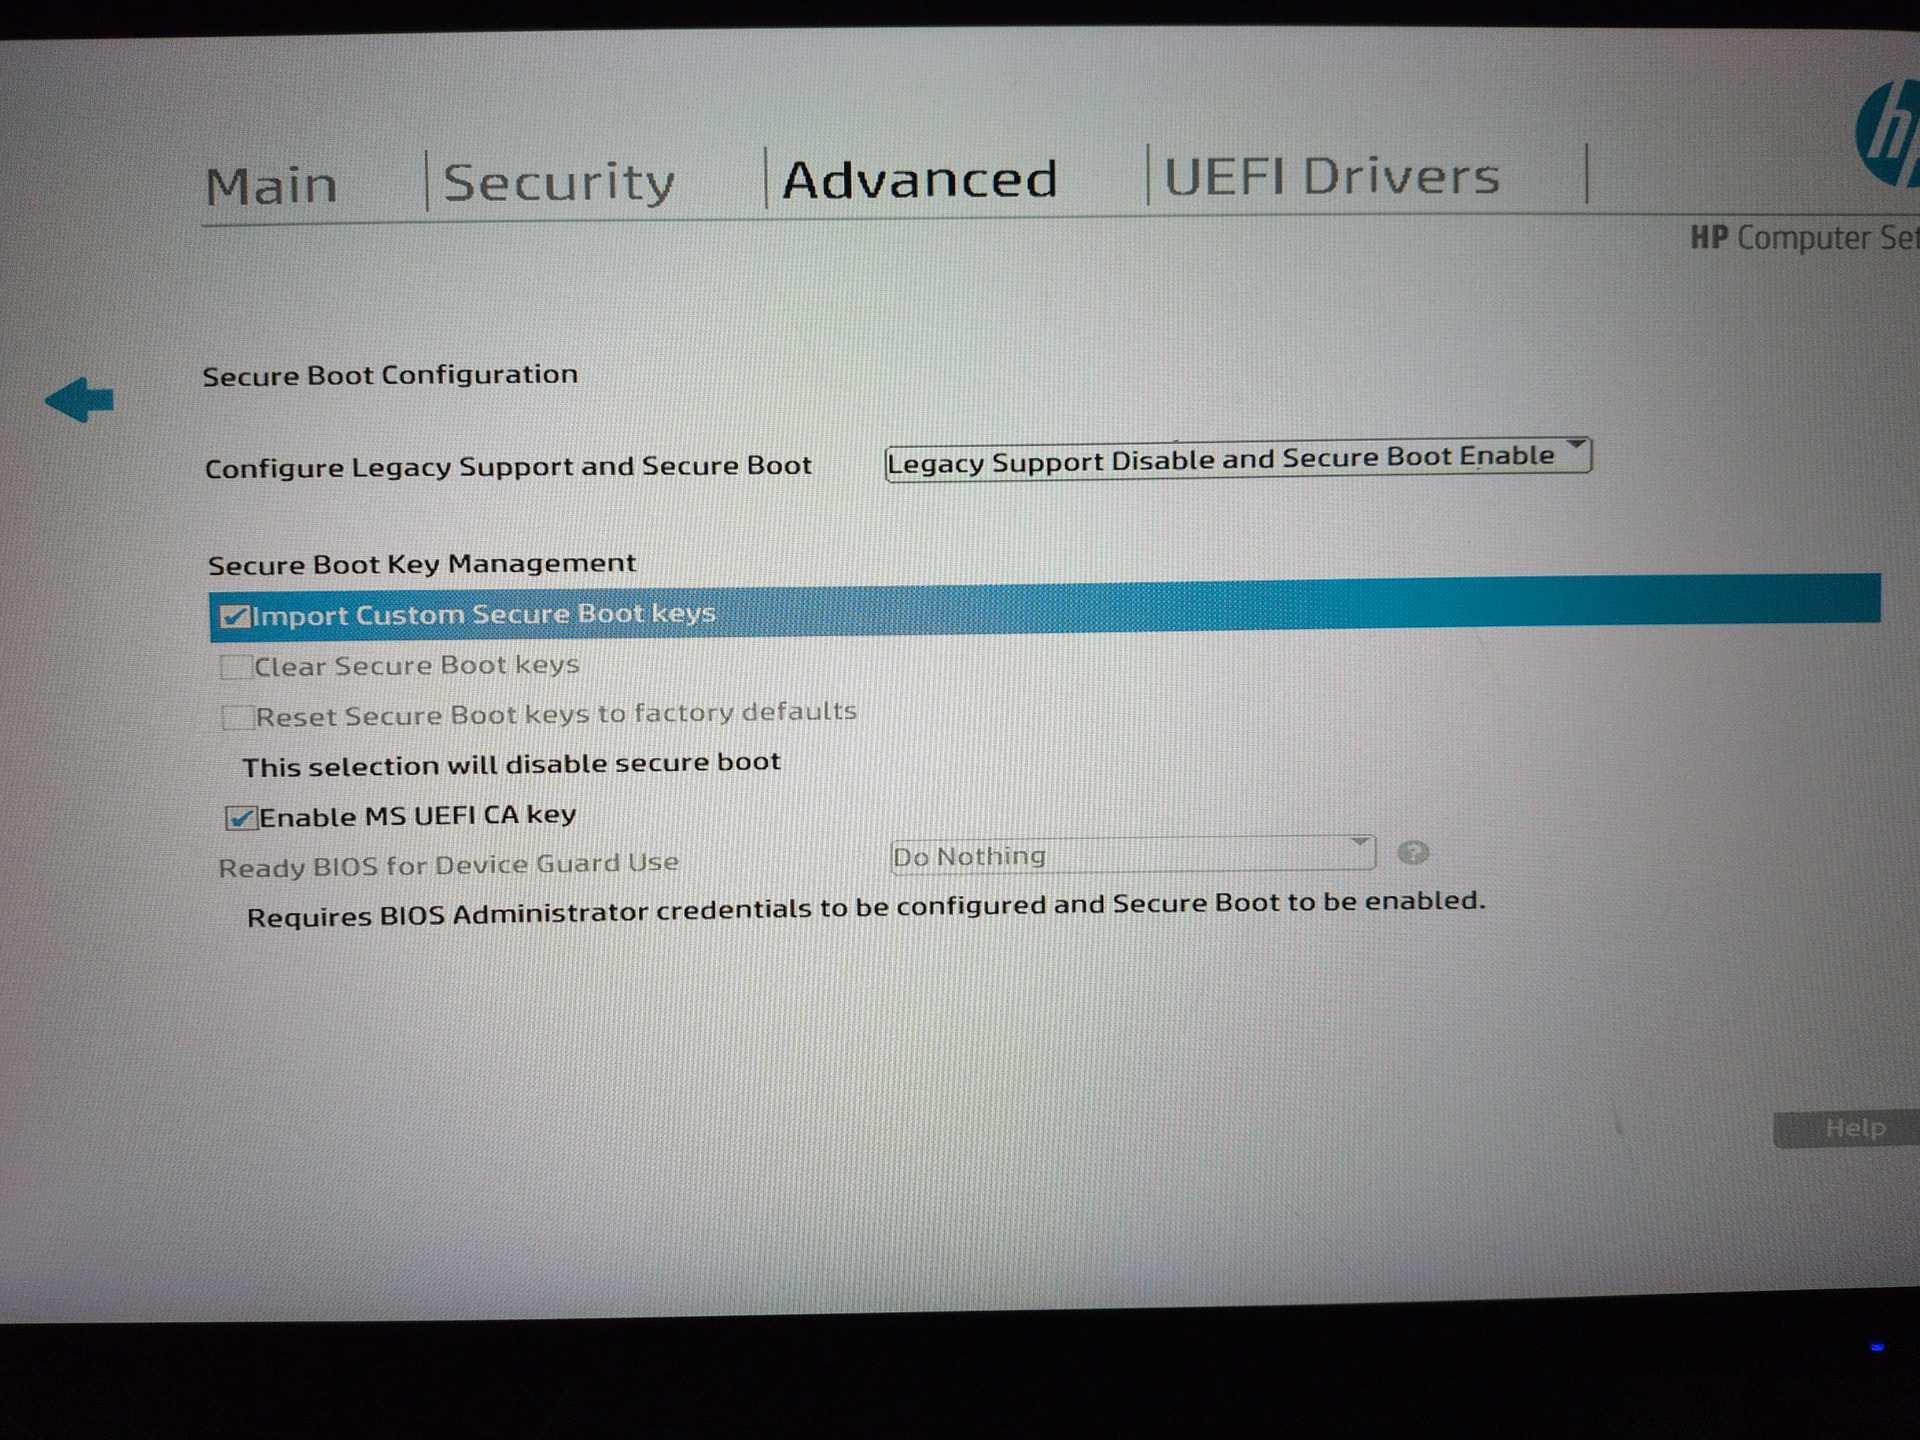
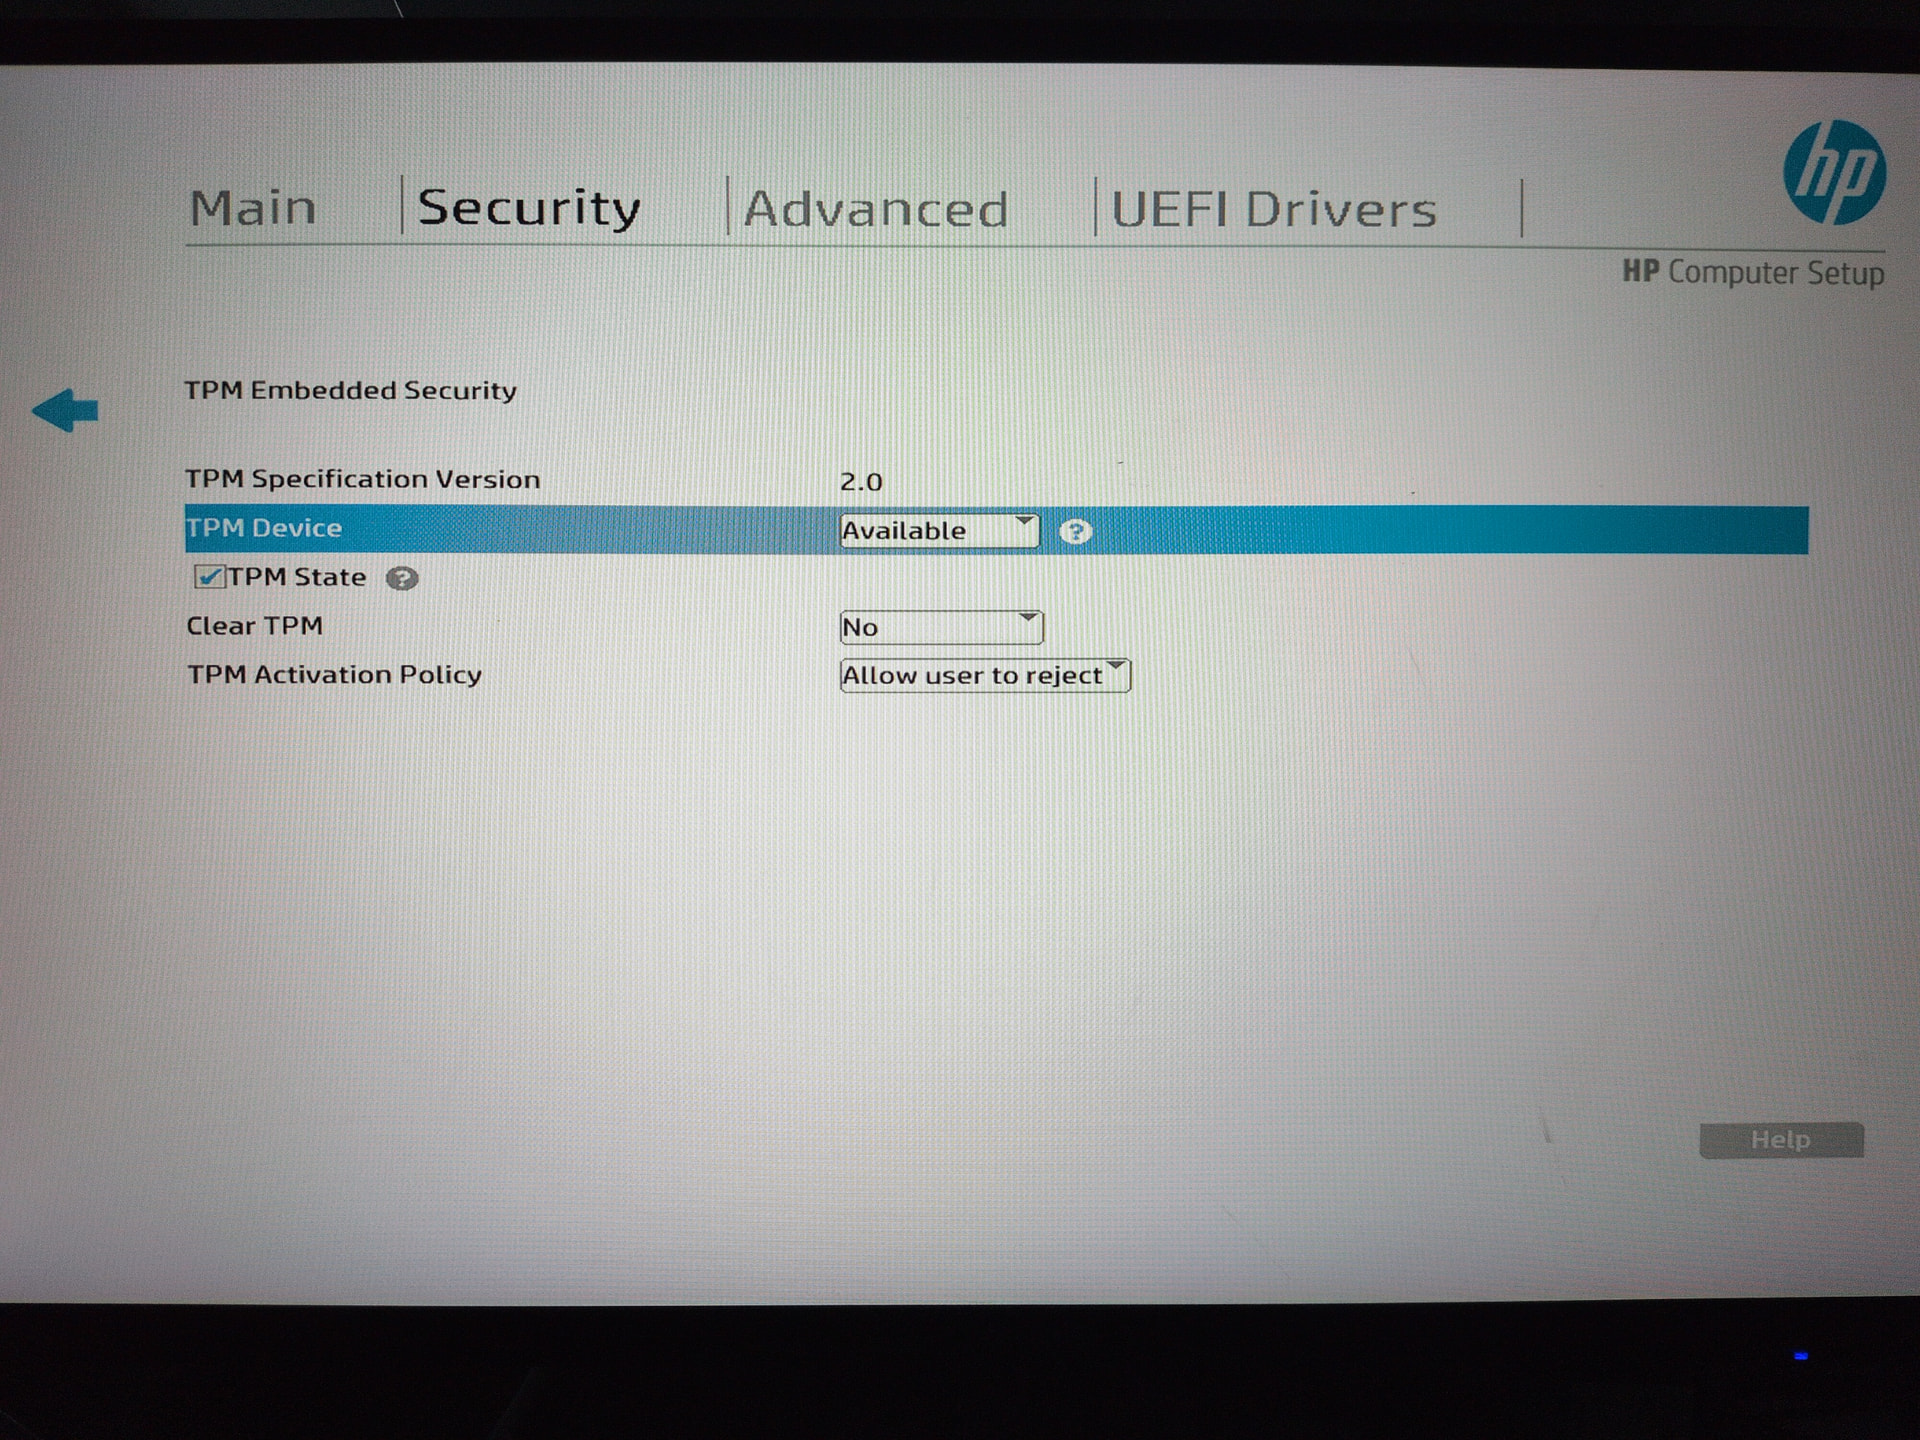
After rebooting, and confirming the Secure Boot change, a reboot only causes a message along the lines of “Image not signed with correct keys.” Apologies, forgot to take a picture.
I then checked the manual, page 28, Section 4.5 Secure Boot Configuration Menu.
The manual states
[…] custom secure boot keys are imported from the EFI\HP directory […]
The custom keys consist of PK, KEK, DB, and DBx .bin files.
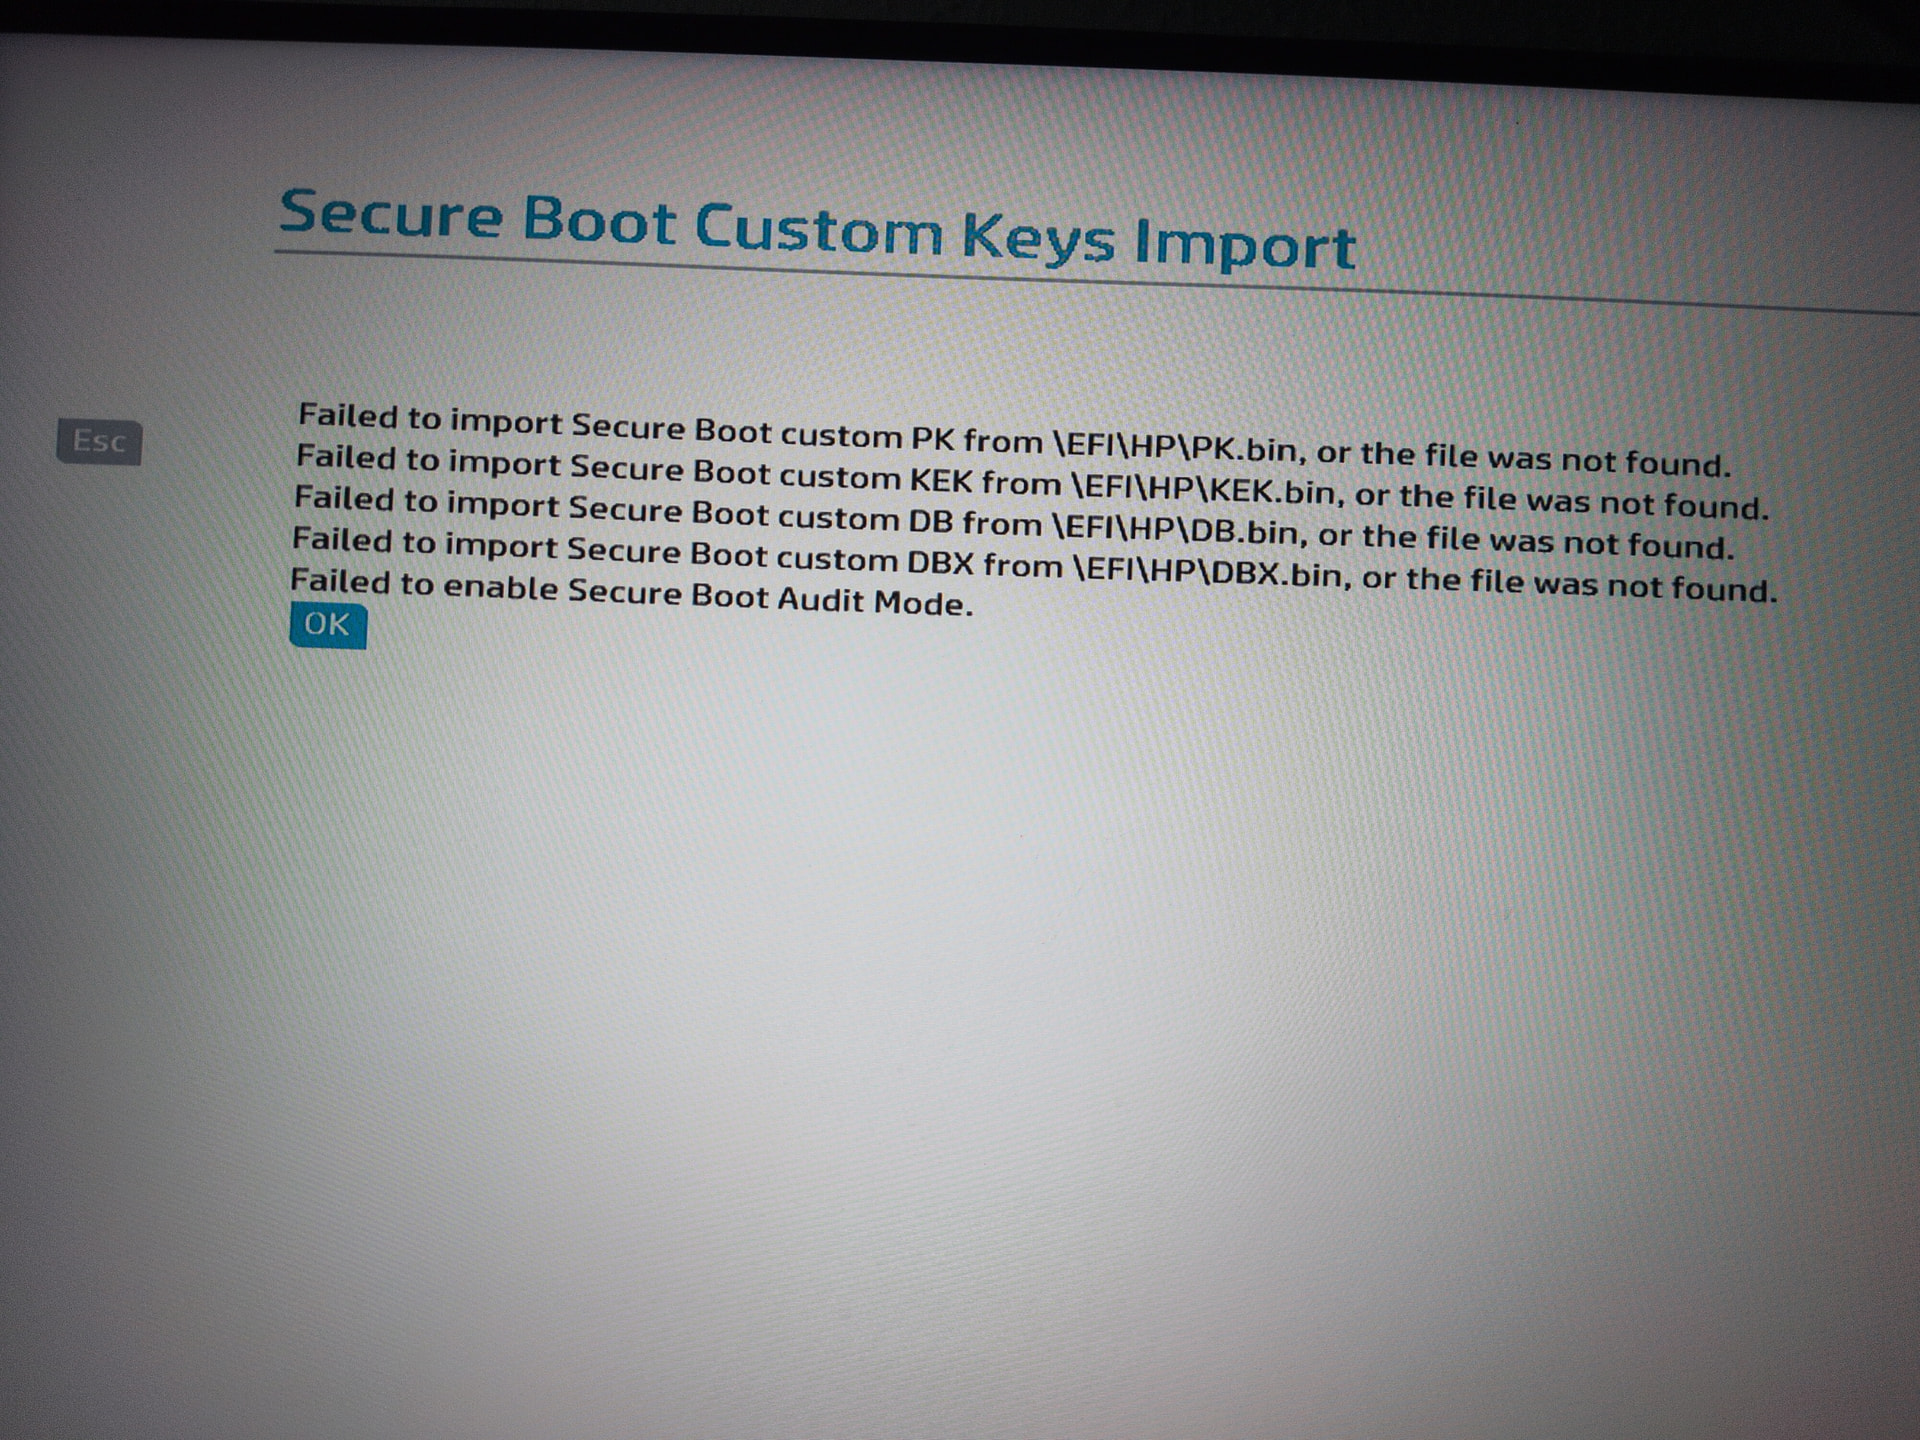
When import succeds or fails, a preboot prompt shows the results of each key bin file.
Following the manuals advice, I moved the keys/ directory into <efi-partition>/HP as well as <efi-partition>/EFI/HP.
I was not shown this preboot prompt in either of these three cases.
The keys/ folder only contains .der files of KEK, PK, and DB. Looking around online I did not find the source of these files, or their .bin equivalents.
If you require any more information, do not hesitate to ask.
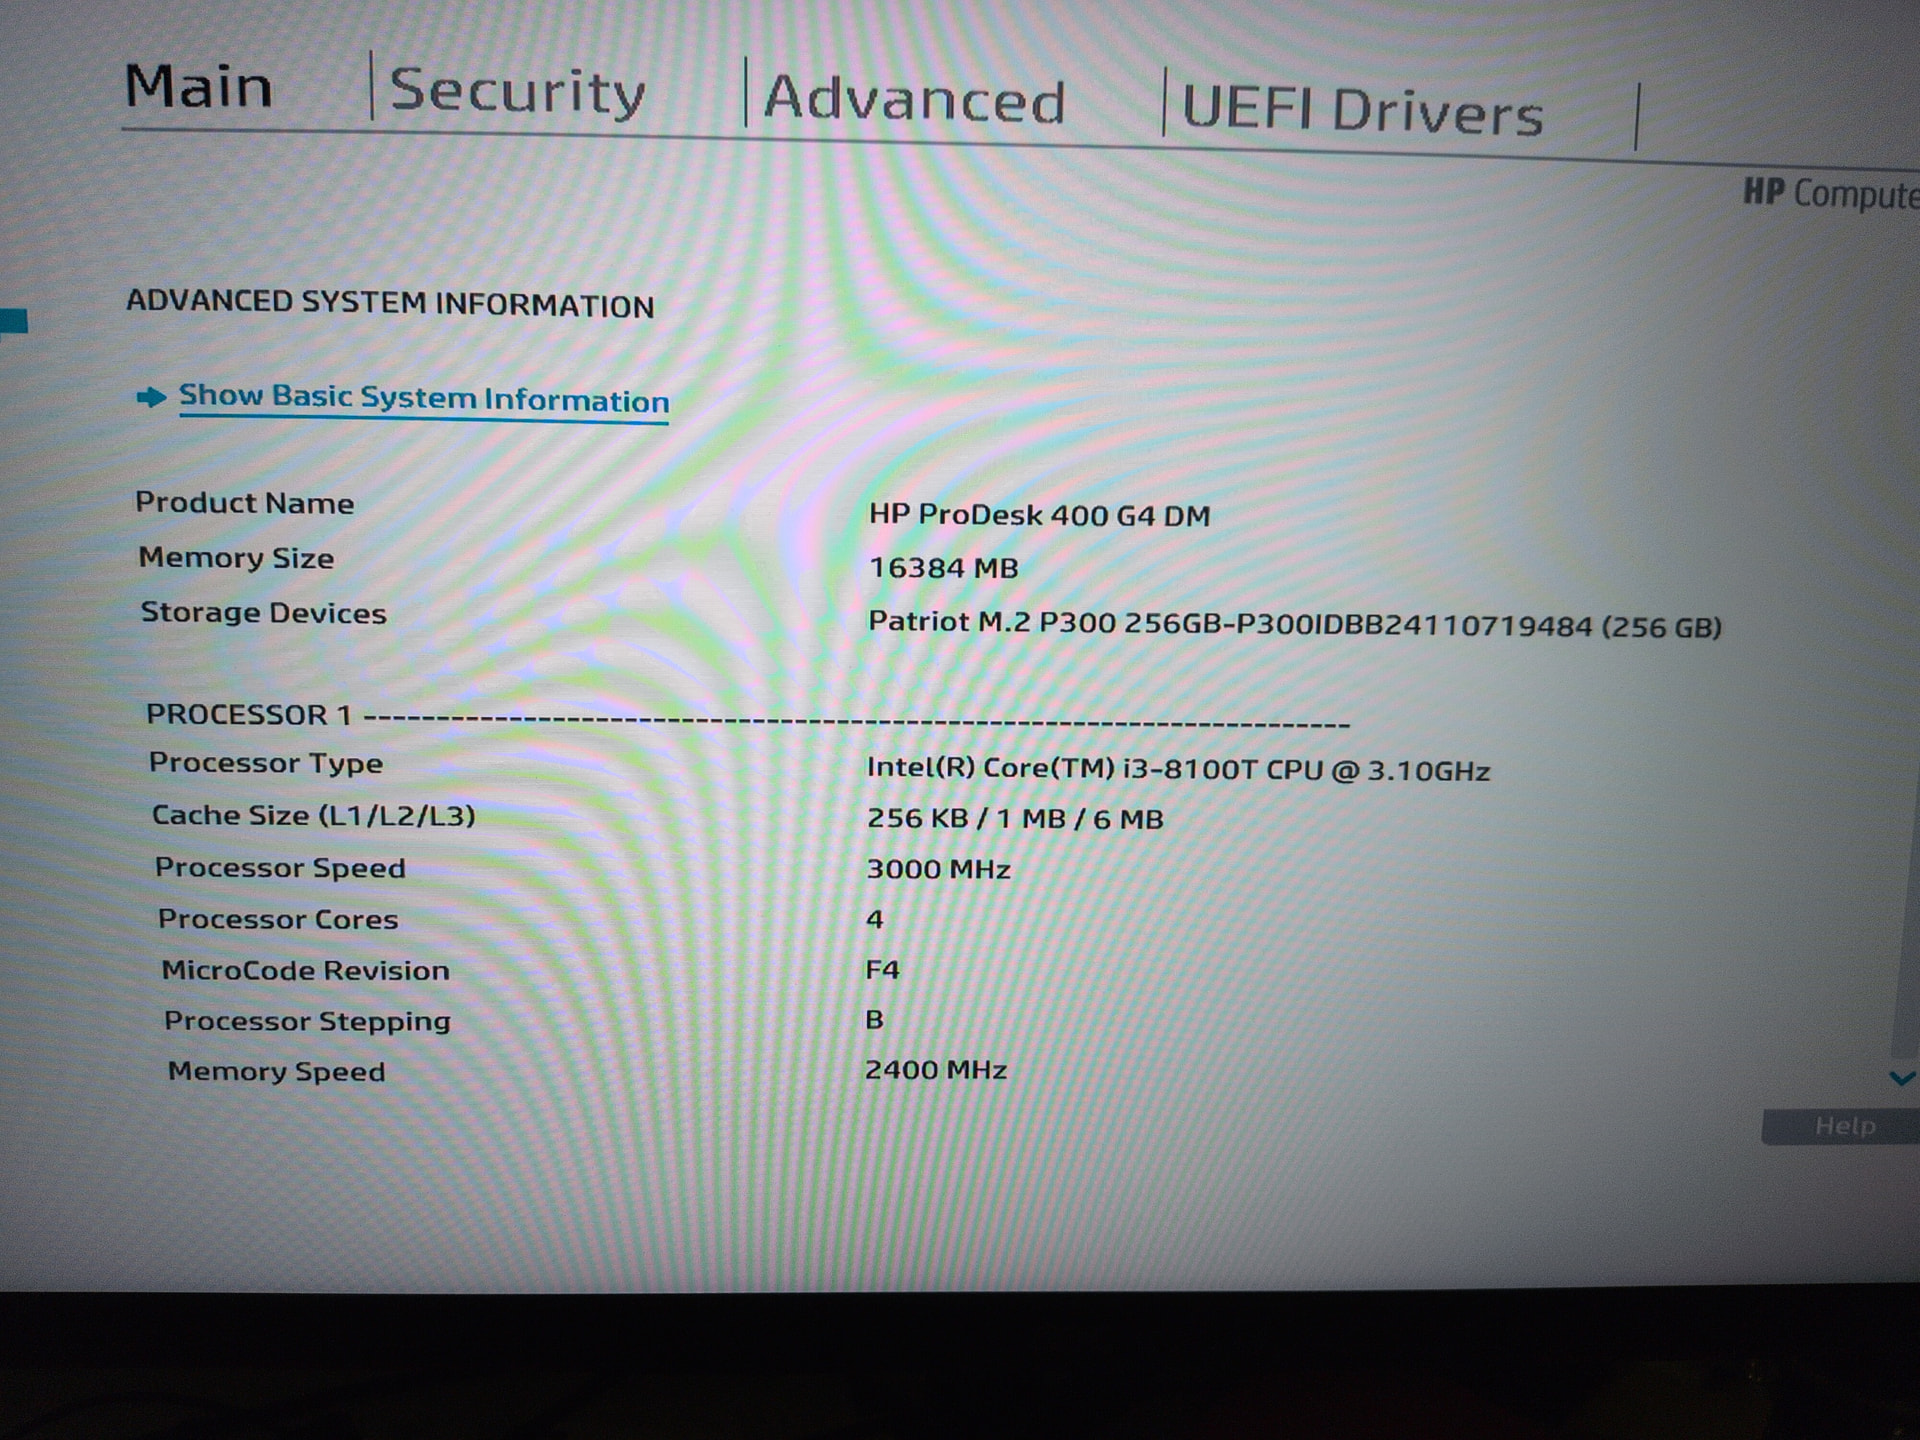
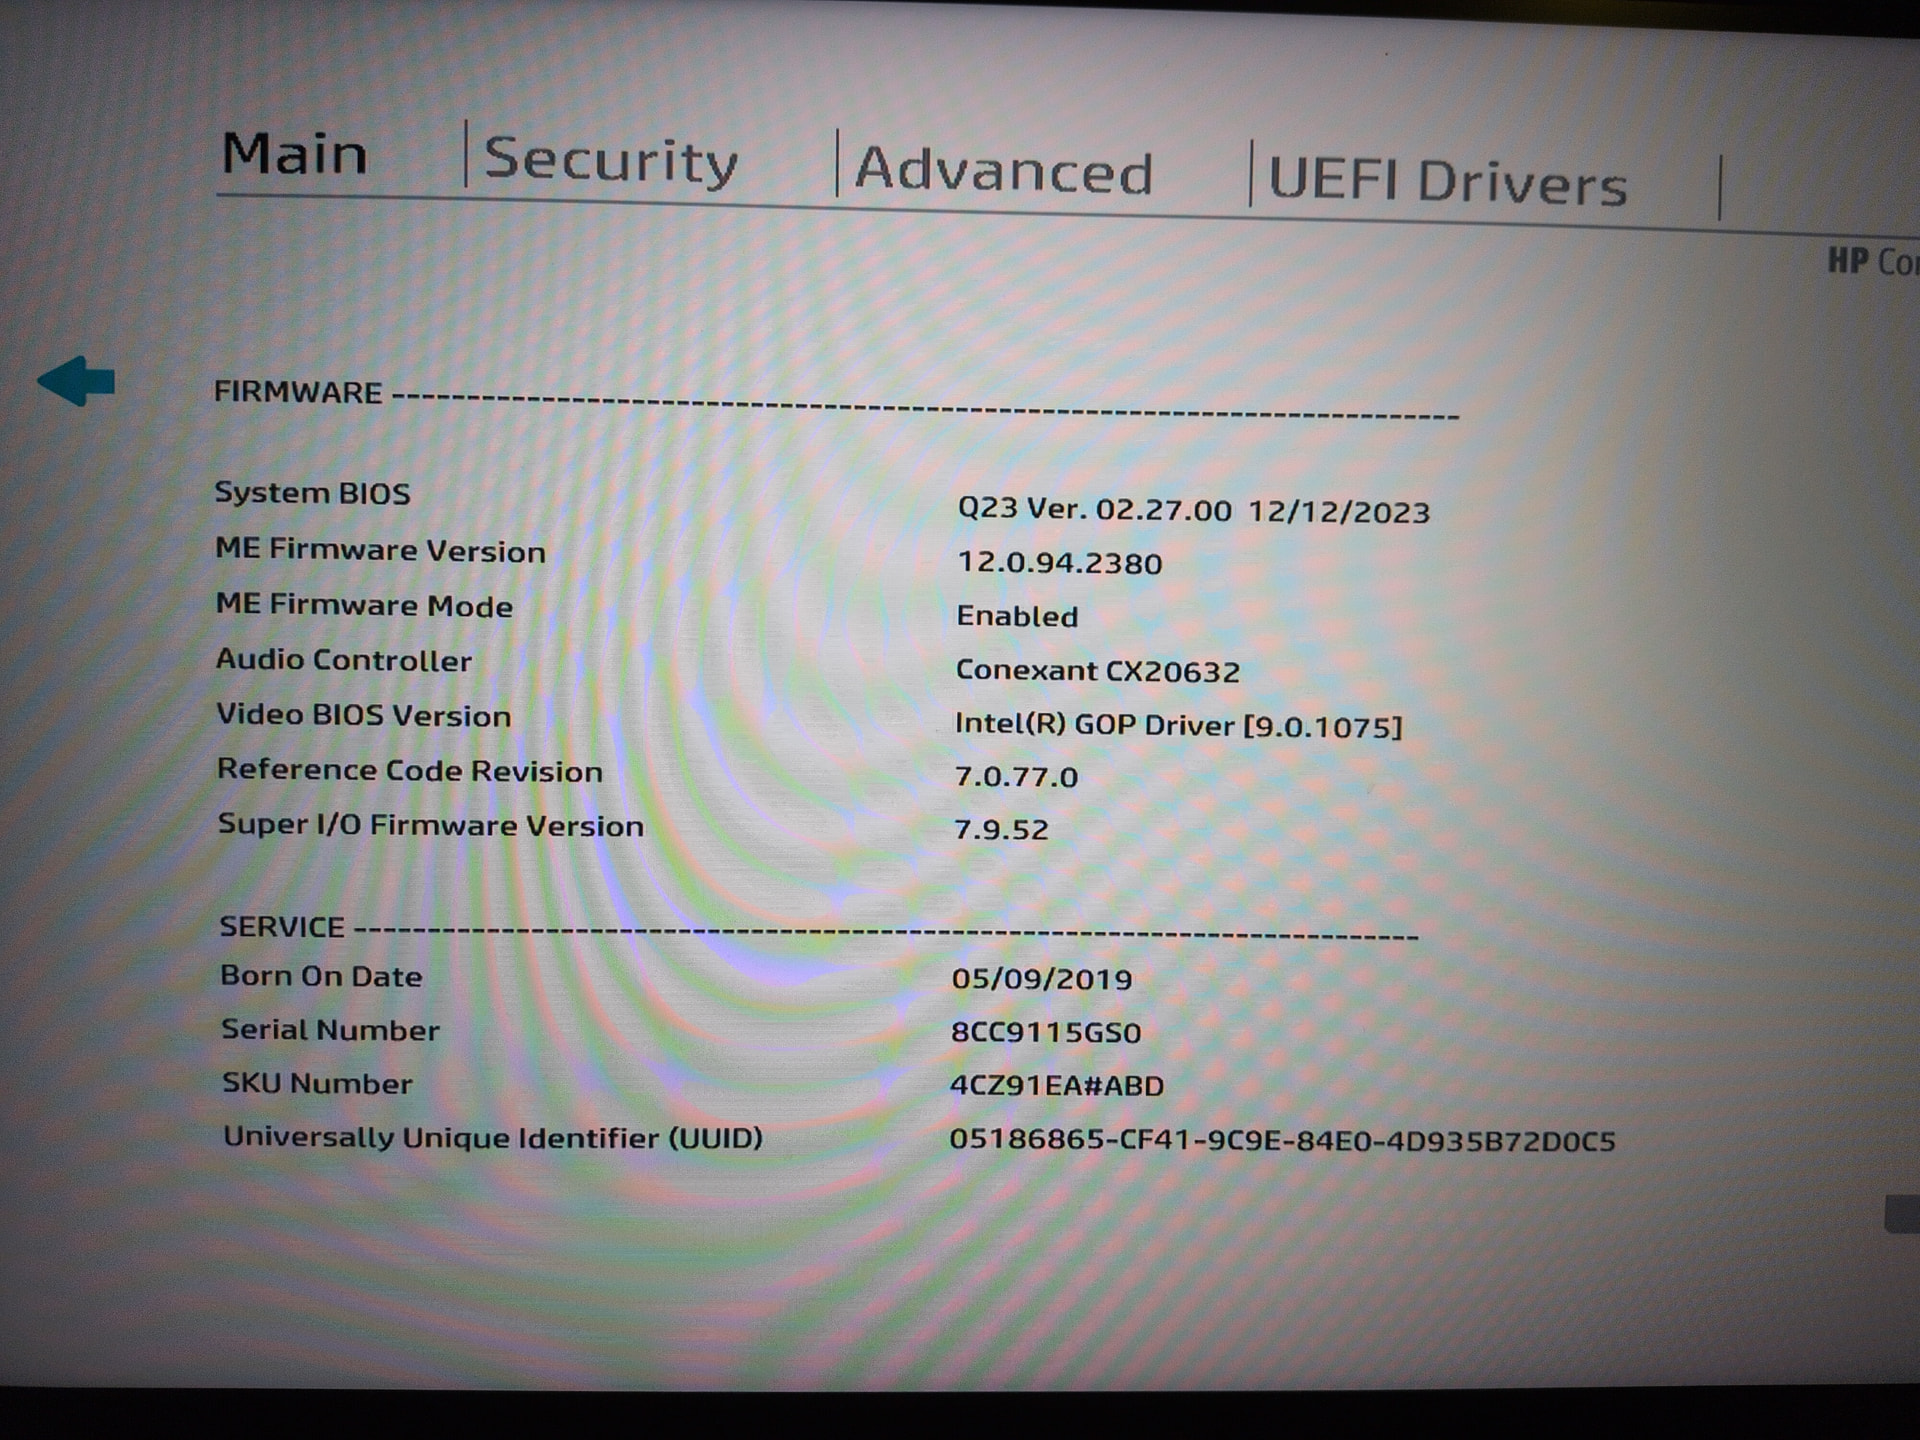
I’m following the same installation path and the missing Secure Boot prompt makes this look like a firmware-specific issue rather than a simple IncusOS setting. The exact BIOS version and whether the machine is using legacy or UEFI-only boot would be useful details when comparing this model with known working installs.
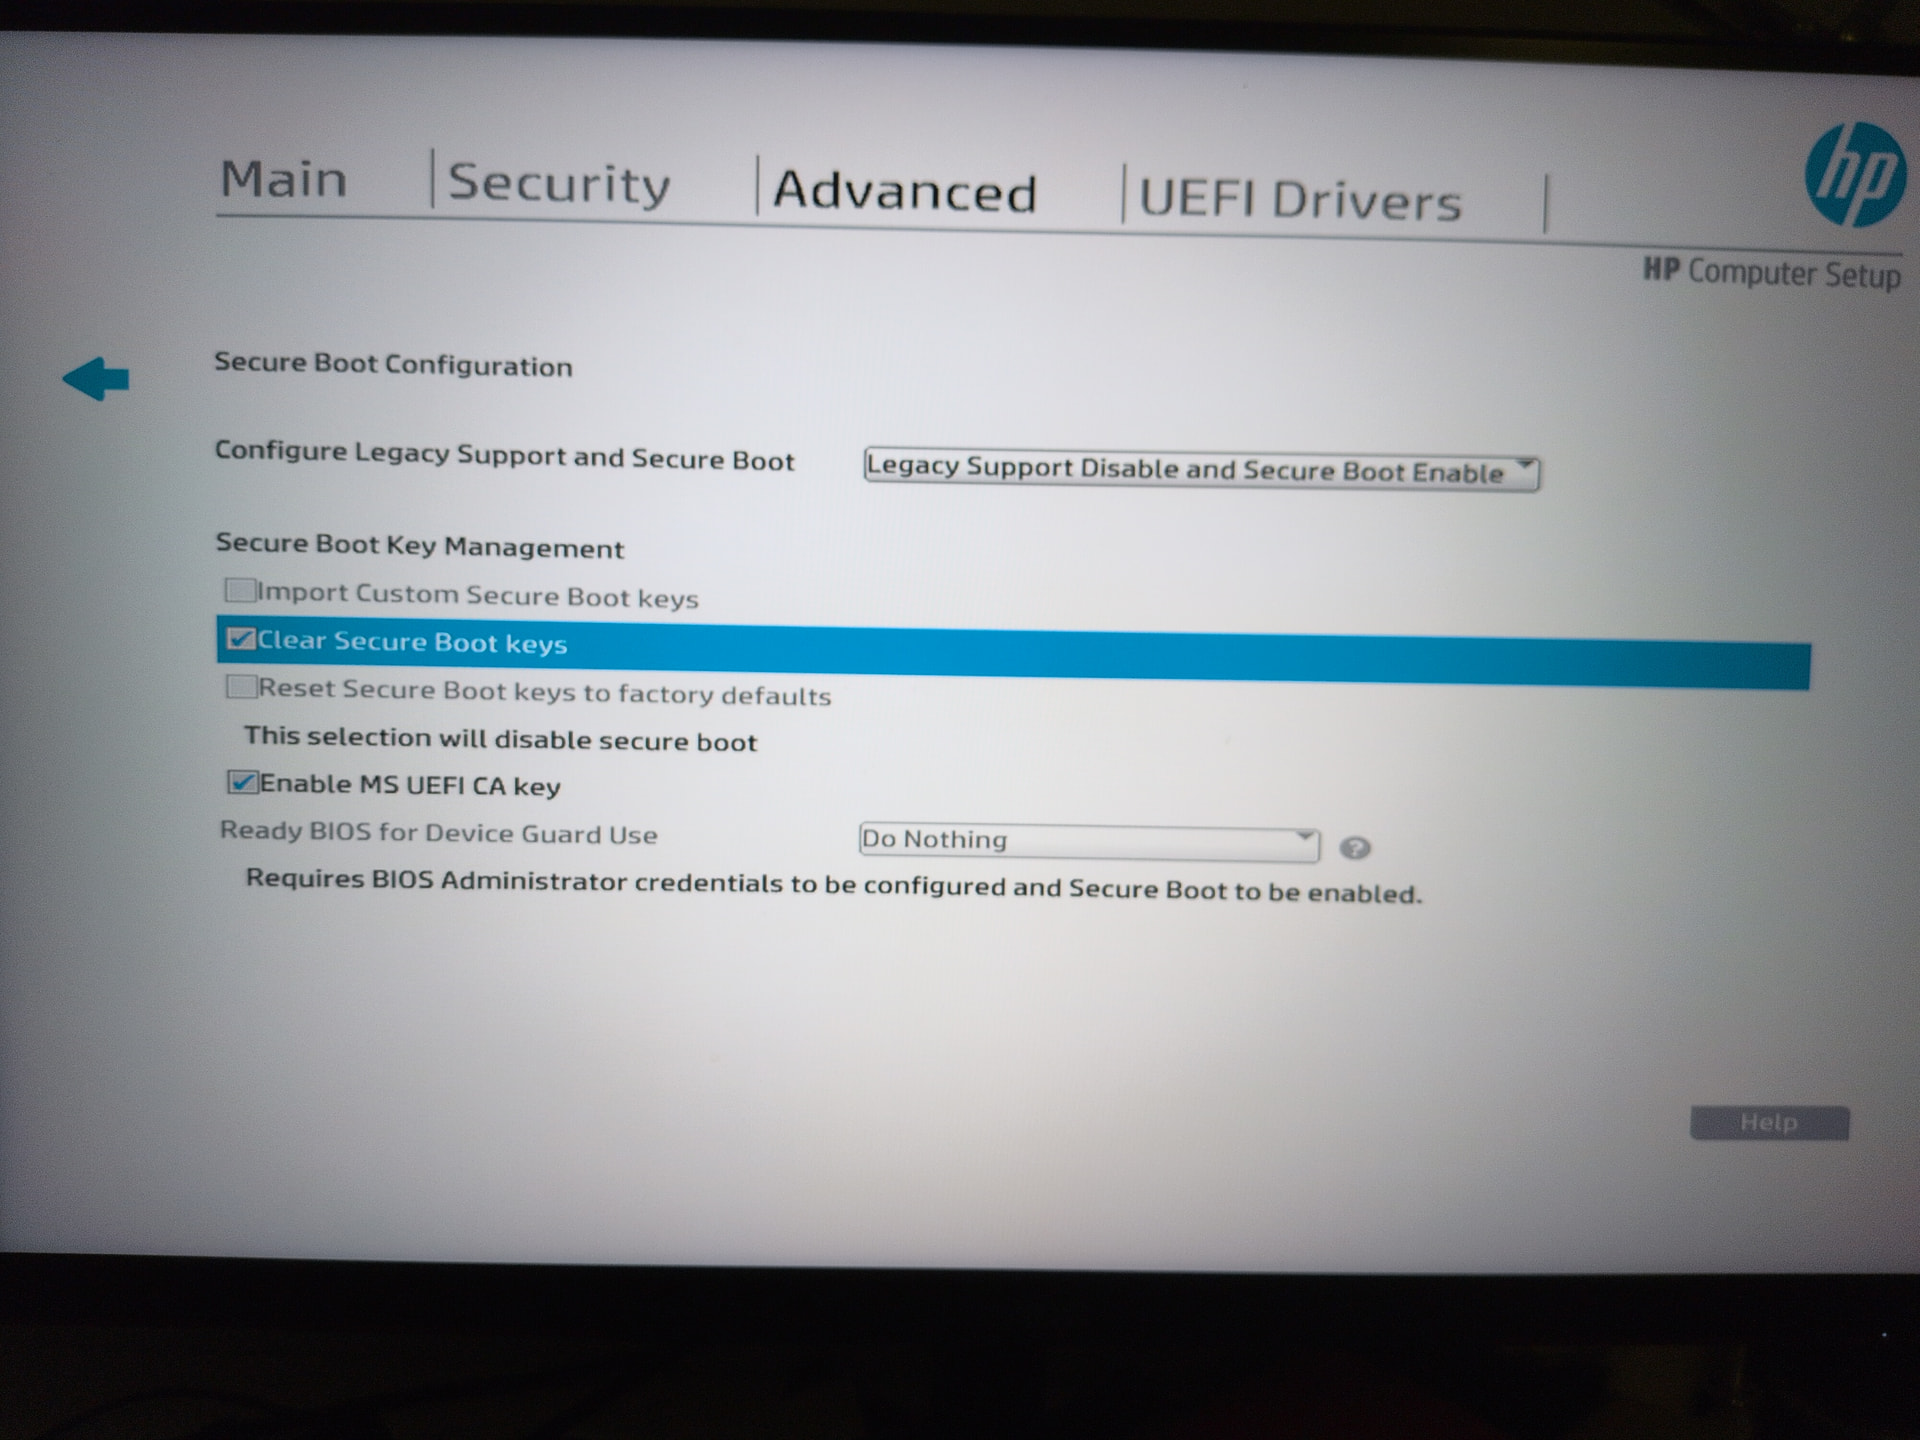
Might be worth trying the Clear SecureBoot keys option. That may be a way to get Secure Boot into Setup mode, which would then provision the keys when you boot from the install media.
In an attempt to follow the HP manual, I moved the .ders from the keys/ into a HP folder, and renamed them into .bins.
This seems to have been more successful, at least the “You are importing a custom secure boot key” screen appeared.
Booting the modified image did not work.
Booting the original image also did not work.
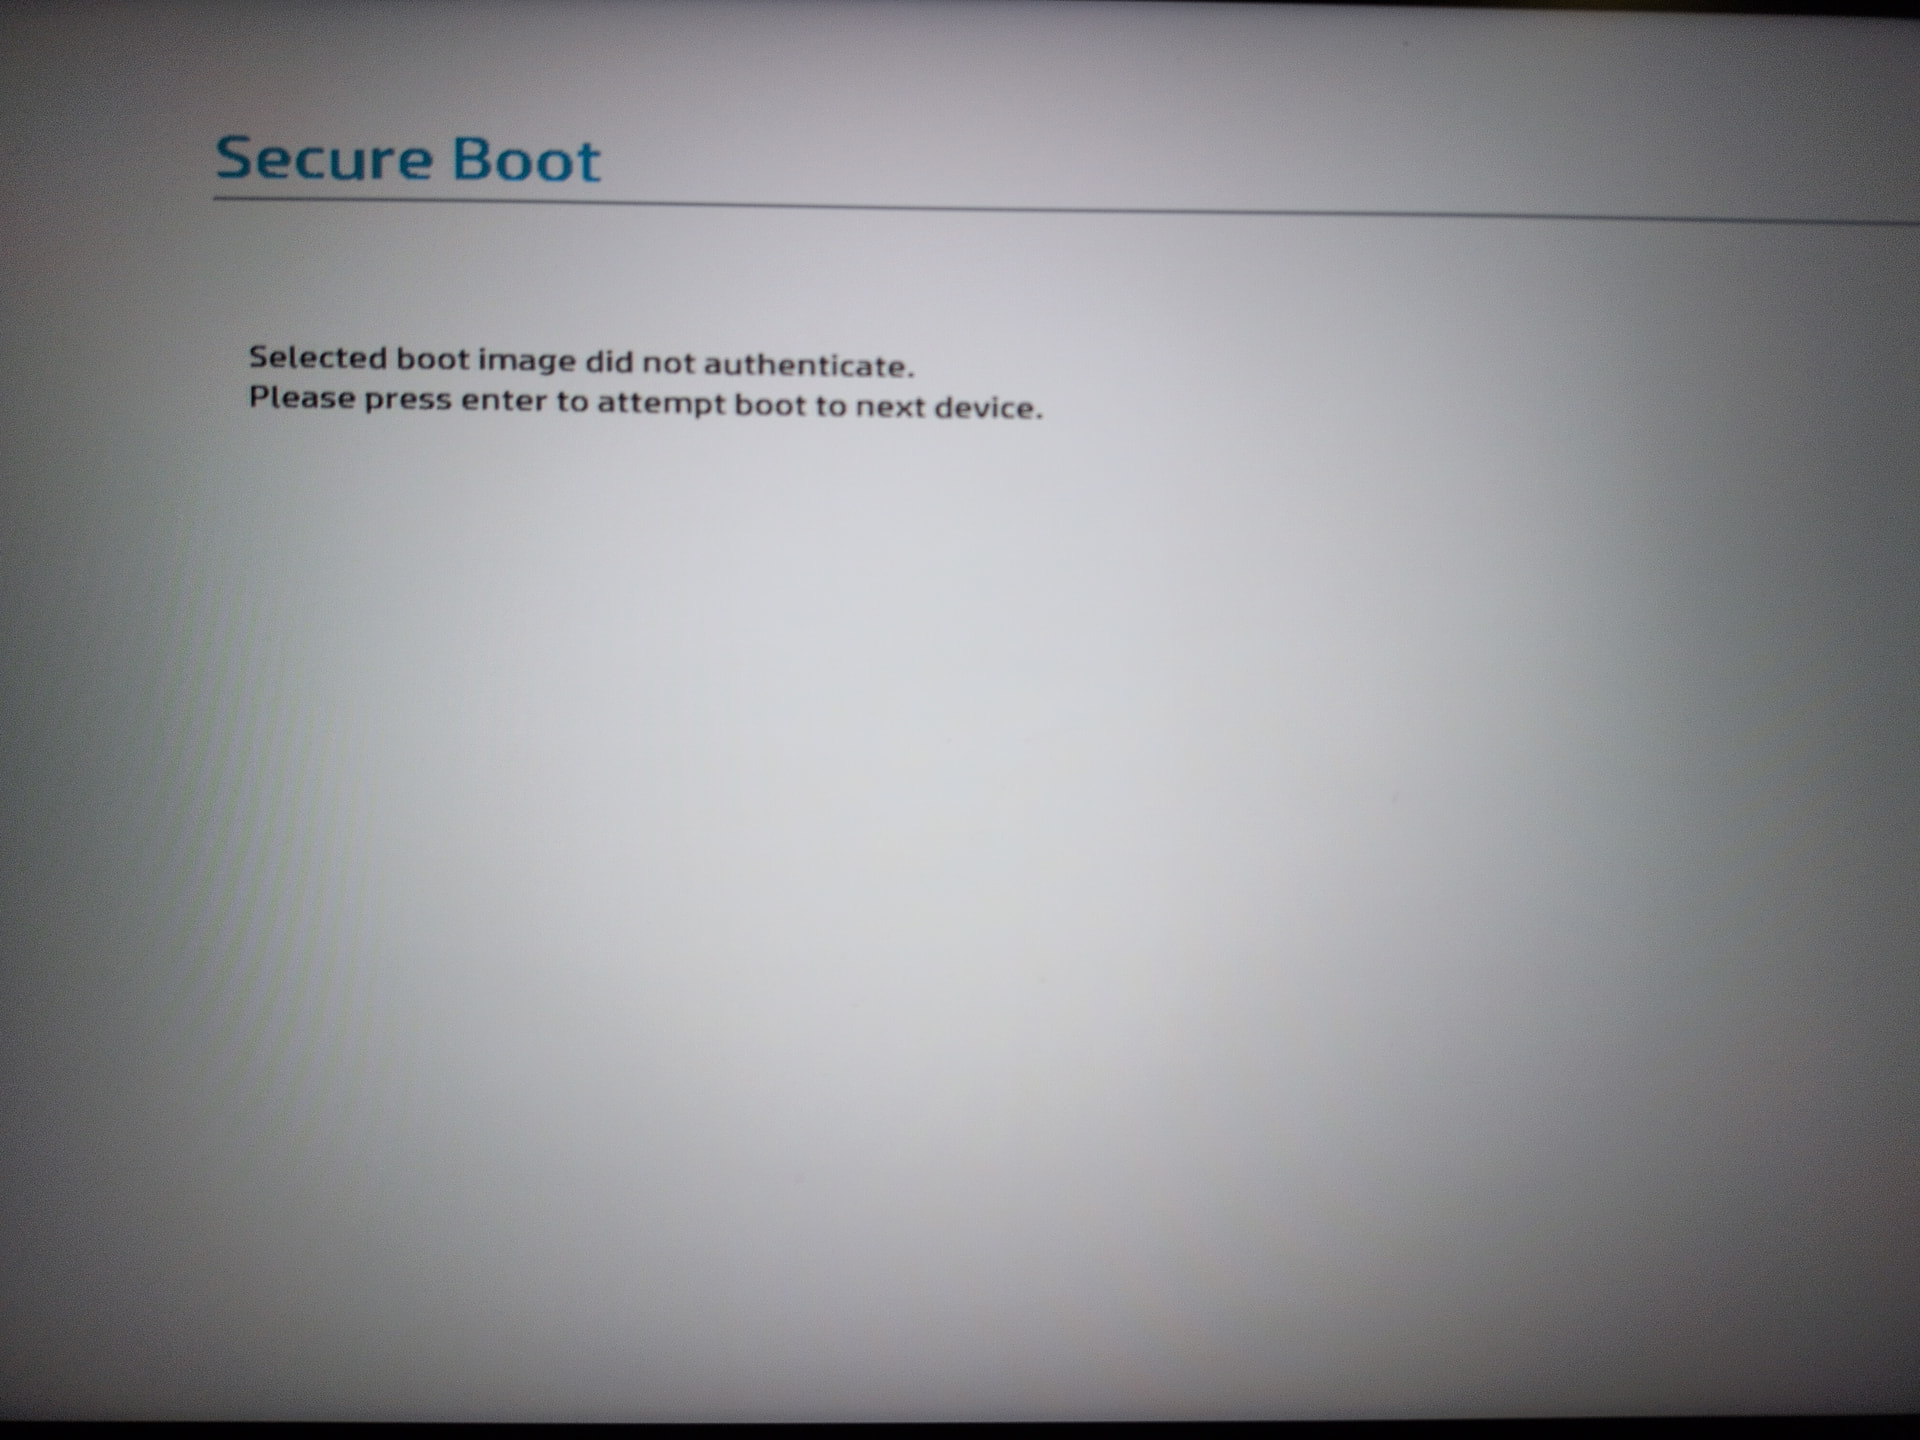
Both got the Selected boot image did not authenticate message.
That particular HP platform seems pretty frustrating from what I could find…
Seems like the way to go is setup mode, but setup mode is weird on this one and needs:
F10 setup → Security (or Advanced on some layouts) → Secure Boot Configuration.
Disable Secure Boot, and make sure “Import Custom Secure Boot keys” is unchecked. Save & exit, and confirm the 4-digit code prompt at reboot.
Re-enter F10, check “Clear Secure Boot keys”, save & exit, confirm the code prompt again.
Boot the IncusOS USB. The firmware is now in Setup Mode, so systemd-boot on the media shows the key-enrollment countdown and enrolls PK/KEK/DB itself.
Re-enter F10 and re-enable Secure Boot (“Legacy Support Disable and Secure Boot Enable”), confirming the code prompt once more.
The 4-digit code thing seem to be some presence confirmation logic that they have in there.
No idea why HP made such a difficult process out of this
Usually we’re used to seeing either the normal AMI based SecureBoot security options (most servers) or the more consumer-grade stuff which relies on a simple setup mode switch.
Here it looks like they’re trying to re-invent the wheel with a very complex way to hit Setup Mode as well as a very non-standard way to provision custom keys (custom HP folder, using .bin files rather than normal file picker and .der or .pem).