My IncusOS installation has been running fine on a fairly modern (4 years old) computer, with TPM2.0 and secureboot enabled.
I’ve had a couple very short power outages in the past week, and I just now noticed that all of my self-hosted services have gone down.
After hooking it up to a monitor, I found that it was “starting IncusOS…” and then it would ask for the encryption recovery key for the root partition, and it does this on every boot. I checked my BIOS settings, everything is the same.
When I enter the encryption key, it continues to the dashboard, but it complains about “swtpm was already configured,” which I’ve never seen before, and it refuses to finish IncusOS startup.
What do you think happened, might it be related to the power blips, and how should I try and fix it?
What version of IncusOS is being booted? Did you triple check that your TPM is still correctly enabled in the BIOS?
It sounds like the system may have booted without the TPM device and created an swtpm state in the EFI partition which is now causing you some trouble.
Anyway, would be good to know more about the system before we starting messing with it too much
I suspect the best way to fix this will be to boot the system onto a live Linux environment of some kind, then mount the EFI partition and remove the swtpm state from it (making a copy of it in case it’s actually needed). That should then boot the system back and using the physical TPM again.
Yes, I have confirmed that the TPM (AMD fTPM) is enabled in BIOS. When I disabled it, IncusOS explicitly said something about “falling back to swtpm implementation”.
My main version (A) is 202609222152, and my B version is 202609100026. Both versions show the same error.
I will try to remove the swtpm state from the EFI partition, if I get lost, I will be sure to ask.
I backed up and then removed the swtpm directory in the EFI partition, and it no longer asks me for the recovery password!
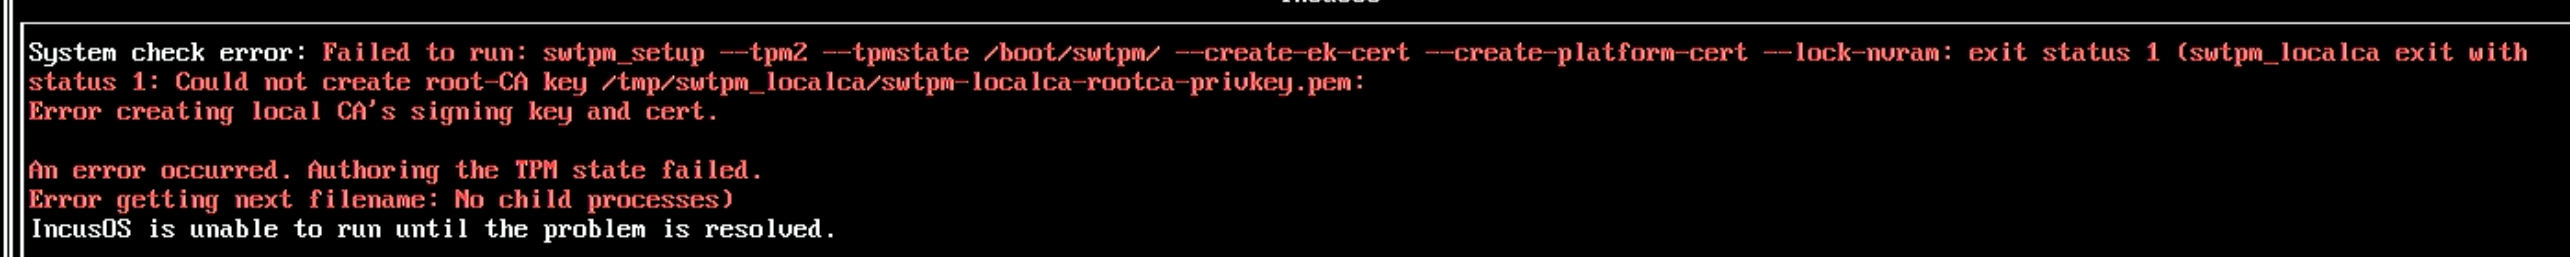
However, in the startup process, it now says something about how using a software-backed TPM will result in degraded security, which is weird, because I’m using a firmware TPM. Then, after that warning times out, it throws an error:
I think I fixed it! I went through the same steps to clear the swtpm state (mount EFI part. and rm -r swtpm), but this time, I rebooted into the old version. And it worked! It did perform an update and then restart, but it still worked after the restart!
What might have happened was that that specific version (202609222152) was causing the swtpm state issue.